Security
How Udon protects your Mac home server with a non-root daemon, HTTPS, strict session cookies, and hashed passwords, and how to report a vulnerability.
Reporting a vulnerability
Email [email protected] with the details and steps to reproduce. Please don't open a public issue for a security problem. You'll get an acknowledgement, followed by a fix or mitigation.
Security model
udondruns as your user, never as root. The actions that need root, such as changing macOS settings, network configuration, and file sharing, go through a separate signed helper that runs only a fixed list of commands. The helper belongs to the macOS account that installed Udon.- Full Disk Access is a separate macOS grant. Installation lists one signed Udon app in System Settings; you enable its switch. Udon verifies the grant from both the daemon and menu bar processes. See Permissions.
- Installation and updates validate the signed release and its components before replacement. An update retains the previous installation and a consistent database backup until the new build passes its readiness checks. See Update recovery.
- The dashboard is served over HTTPS, with a certificate Udon creates on first run. Other sites can't embed the dashboard in a frame, and terminal and remote desktop connections must come from the dashboard's own address.
- Session cookies are HttpOnly and SameSite=Strict, so other sites can't send requests with your session. Sessions end after 12 hours, or 30 days with Keep me signed in on this device, and repeated failed sign-ins lock the username for a minute.
- Passwords are stored hashed. Secrets such as provider API keys and the MCP token are kept in files only the daemon can read.
- Udon is reachable on your local network. Exposing it to the internet is a deliberate choice and isn't recommended; reach it remotely over Tailscale instead.
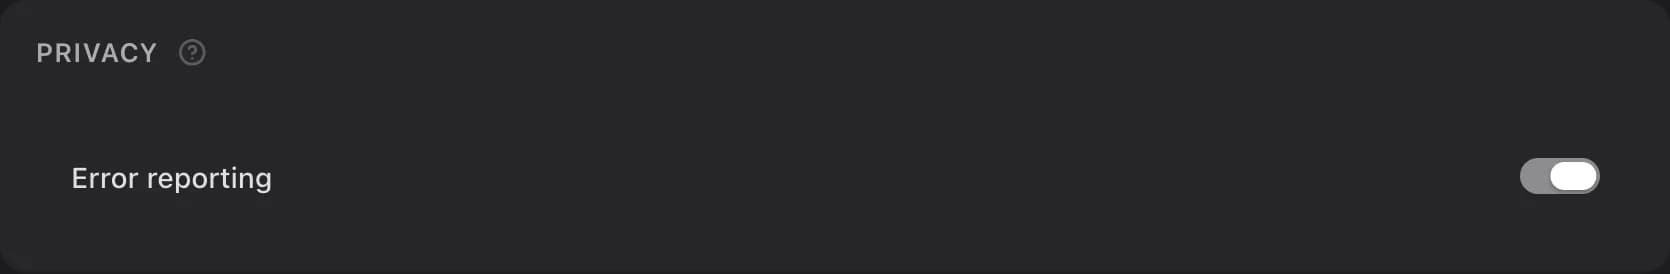
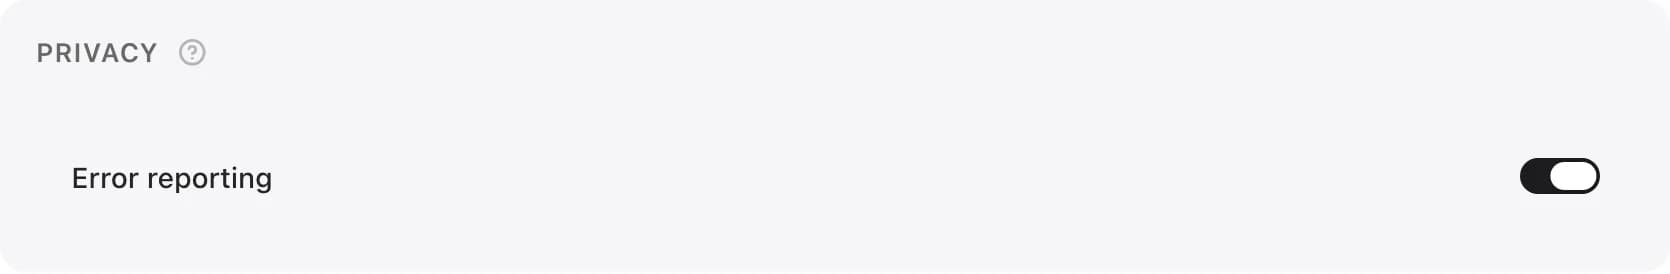
- Error reporting is on by default while Udon is in beta. It sends anonymous crash and error reports, a coarse hardware profile, and a daily usage heartbeat, never personal data, file contents, or IP addresses. The setup wizard asks whether to share them, and an admin can change this with Error reporting in Settings → General → Privacy; it takes effect at once, and Udon says so if the change fails.